Today's cars are computers on wheels, and the supply chain behind them depends on a constant flow of shared data, from designs and prototypes to production schedules and customer details. A single weak link can bring the entire operation to a standstill. Jaguar Land Rover learned this the hard way in 2025, when a cyberattack shut down production for weeks and left its suppliers struggling. Even so, information security in the automotive sector rarely gets the attention it deserves.

Base27 gives automotive organisations a structured and manageable way to handle information security. With everything in one clear platform, you can identify your risks, comply with frameworks such as TISAX® and show at any time that your processes are under control.

Calamiteitenplannen

100% EU based 

Your data is in safe hands. Fully GDPR-compliant with local support. 

Beleid en organisatie

250+ Happy customers

Join a growing network of organisations that trust us to keep them secure. 

Operationele planning

50% time saved

Speed up your workflows and free up yout team to focus on what really matters.

The challenges of information security in automotive

Automotive runs on collaboration and precision. Every day, sensitive information flows between manufacturers, suppliers, engineering firms and dealers, while production lines leave little room for delay. Information security simply hasn’t kept up. Without a structured approach, blind spots appear fast, and one disruption can ripple through the entire chain. Toyota found this out in 2022, when a cyberattack on supplier Kojima Industries forced it to shut down all fourteen of its plants in Japan. 

The real risk is often closer to home than you might think. It rarely takes a sophisticated attack. A colleague clicking on a phishing email, a recycled password or an unsecured laptop is usually all it takes.

Meanwhile, the bar keeps rising. Car manufacturers now expect their suppliers to hold a valid TISAX® label, and under the Cybersecurity Act (NIS2), motor vehicle manufacturing is classed as a critical sector. Falling short can mean fines, a damaged reputation and missed contracts.

2-1
3

The use of ISMS software in automotive

Information security in automotive rarely stays within one department. Engineering, production, purchasing and IT all play a part, and so do the external partners you rely on. Before long, things become fragmented. Policies end up scattered across documents, risks live in separate spreadsheets and every new assessment means hunting for evidence all over again.

Base27 puts an end to that. With policies, risks, incidents, suppliers and audits all managed in one central place, your TISAX® assessment becomes a structured process rather than a scramble. And when the auditor arrives, everything you need is ready to hand.

Dashboards &
Reports

  • Comprehensive reports giving you insight into the status of your information security at all times;
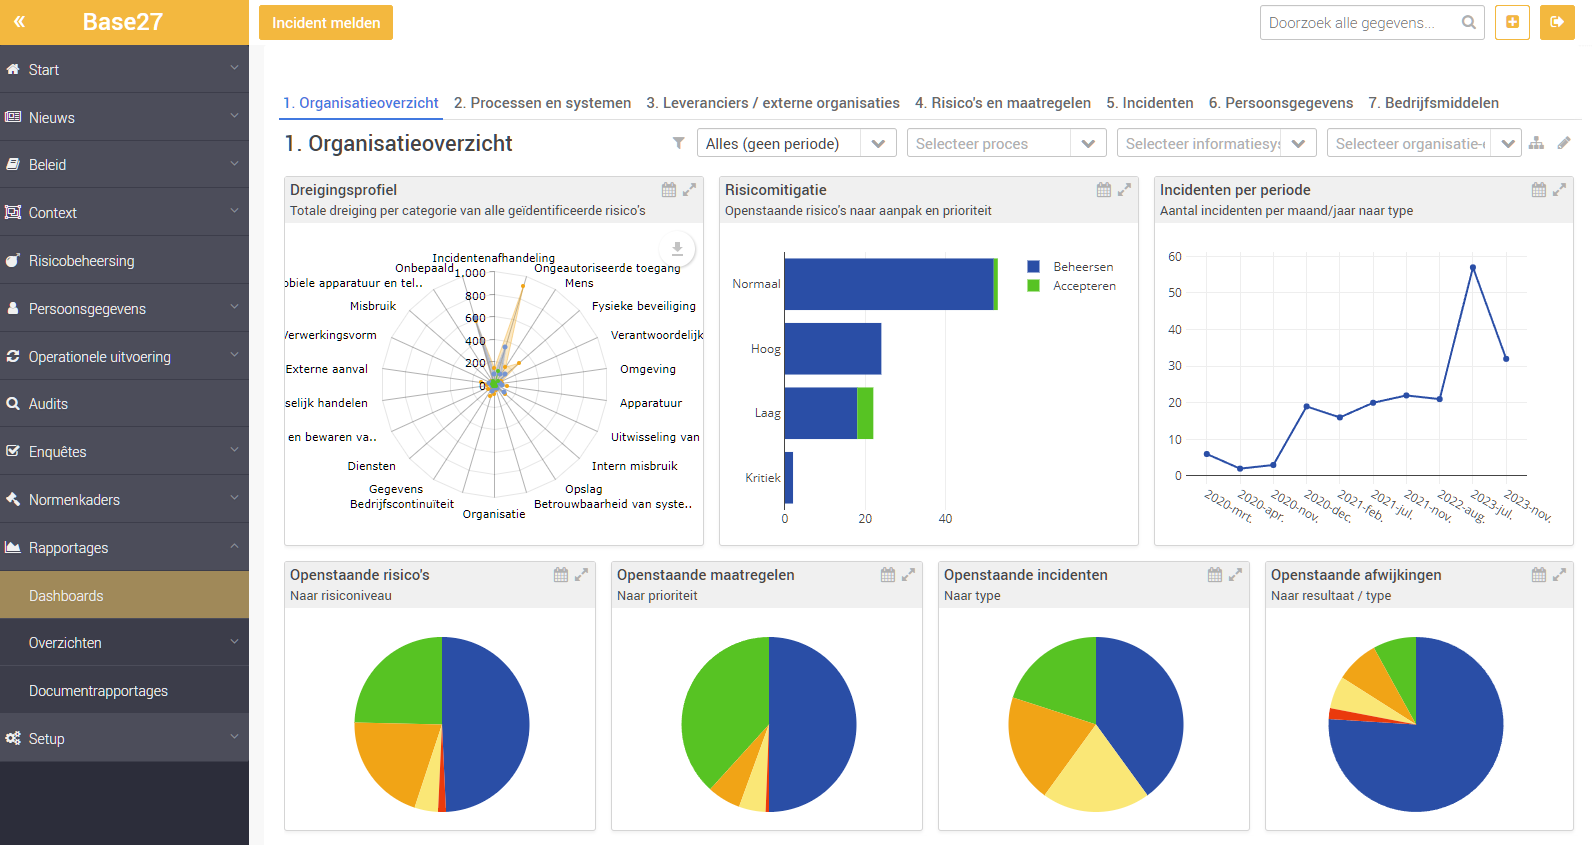
  • Dashboards for quick and easy insight into the status of your information security;
    • Insight by department, or across the board;
    • Filters and sorting;
    • Exports to Microsoft Excel or Word;
    • Analysis in pivot tables.


NL - Dashboard

Planning

  • See at a glance which information security maintenance tasks need to be performed throughout the year and what the status is;
  • Easily assign tasks and monitor progress;
  • The plan can be flexibly expanded and repeated annually.
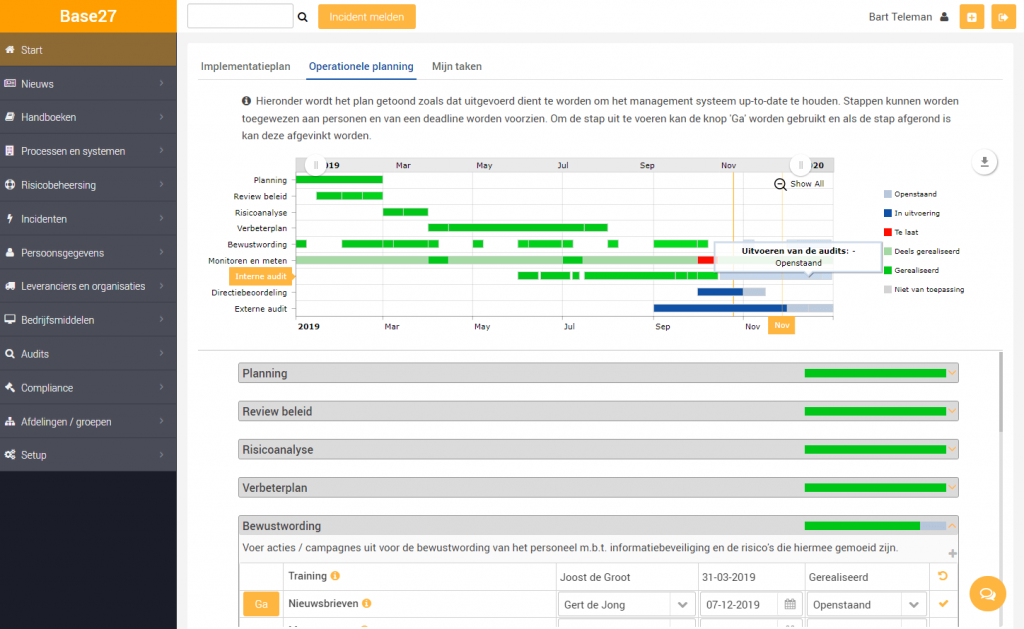
 

operational-planning-Base27

Processes & KPIs

  • Establish overview of processes and related information systems;
  • Set and manage critical success factors and KPIs (Key Performance Indicators);
  • Compliance with standards is automatically made transparent.
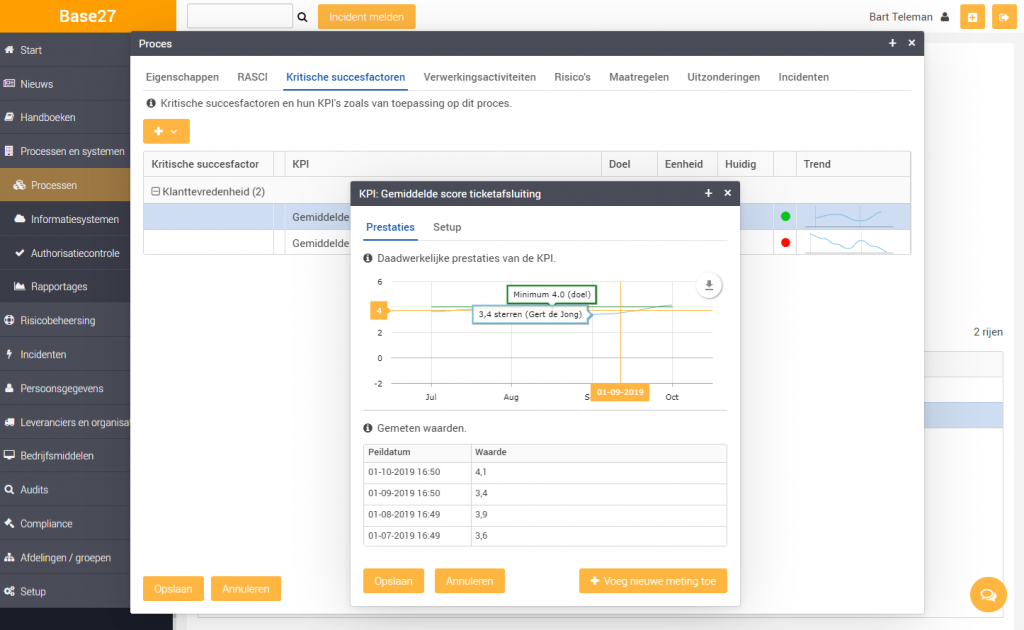
 

process-kpi-base27

Single Sign-on

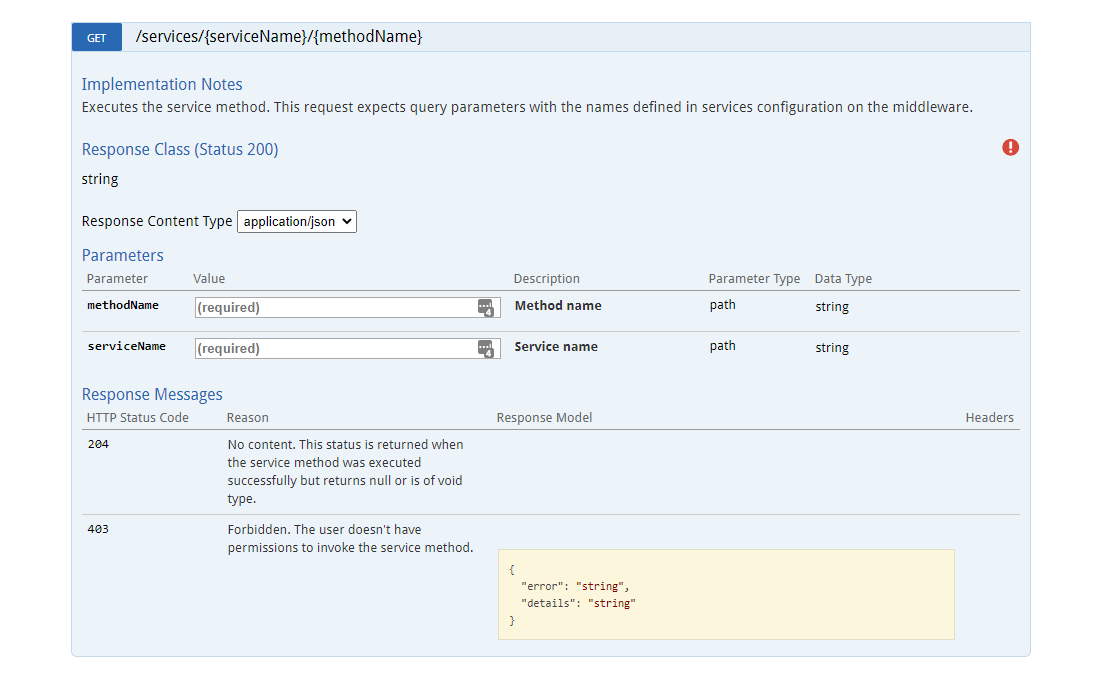
  • Base27 is excellent for integrating within your organisation, for example by using SAML, to allow your employees to access the application without logging in again;
  • REST interface to link data from other sources. Through this capability, incidents from for example your ITSM can be read in or updates sent.
 

RESTAPI-Base27-Single-Sign-On

You don't need to be an expert to get started with Base27

With ready-made structures, clear guidance and intuitive workflows, anyone can get up and running with Base27. The system walks you through every step: spotting potential risks, putting the right measures in place and deciding who is responsible for what. All at a level that suits your organisation, whether you’re a supplier or a dealership.

3-1
Surf-logo
duvak
Iso-secure-logo
Inkesta
SGL
Stichting ZiZ
Vivantes
cloudseven icon
juriblox
logo-provincie-Zeeland
ArQive
vcare-logo

Our first supplier ever that is always ready to help out and understands our objectives

Raoul Vernede

Easy and useful solution for managing our ISMS

Dave Kerstens

Base27 makes compliance clear and simple to enforce

Eildert Karstens

Complete ISMS, excellent support and helpful with internal audits

Sanne Muskens

Very customer-oriented with a good and quick response to questions

Wim Houben

Customisation options, patience in guidance, talent to make the impossible possible

Karin van der Han

Risk management and incident registration  are very useful

Lars Schiltmans

Support for the complete cycle of the ISMS

Marc Kuiken

No-nonsense and clear solution

Jacco Rens

Base27 is the first ISMS that truly aligns seamlessly with the ISO 27001 standard and is very user-friendly

The presence of a complete structure and templates helps enormously with the certification

Marcel Kruithof

Clear all-in-one package

Frank Schonewille
1-1

Why Base27?

Developed in the Netherlands by an international team, Base27 runs entirely on European servers. That’s good news for GDPR compliance and for keeping sensitive design data safe, and it means you’re no longer reliant on American tech giants.

Whether it’s risk assessments and policies or supplier management, incident registration and internal audits, it all comes together in one clear platform. The result? You work more efficiently, stay on top of everything and can show at any moment that you’re in control.

Always in step with the latest TISAX®, ISO 27001 and IEC 62443 requirements, plus other key frameworks and legislation for automotive, such as the Cybersecurity Act (NIS2). Updates are applied automatically.
Structured workflows and a ready-made policy framework that save you valuable time.
Hosted entirely in Europe, so you're fully covered under the GDPR.
Expert support as you prepare for your TISAX® assessment and ISO 27001 certification.

ISMS for the
automotive sector

Base27 monitors and manages your processes from one central place. It serves as both an information security management system (ISMS) and a privacy management system (PMS), giving you a firm grip on the many complex aspects of information security and privacy protection.

From policy development and communication to risk analysis, controls and asset registration, Base27 covers it all.

Try Base27 free for 30 days and discover how information security can finally become clear and organized.

Establishment and communication of policy
Description of processes and procedures
Protection of personal data
Conducting risk assessments and treatment plan
Managing suppliers and partners
Registration of assets
Incident registration and handling
Maintaining calamity plans
Planning improvement activities and internal audits
Monitoring and reporting

Frequently asked questions

What is information security in the automotive sector?

In automotive, information security is about keeping sensitive information out of the wrong hands and safe from disruption or misuse. That includes designs, prototypes, production data and customer details. It covers the protection of production systems and connected vehicles as well.

Which frameworks and laws apply to the automotive sector?

For suppliers, TISAX® is the key framework, built on the foundation of ISO 27001. On top of that, organisations have to deal with legislation such as the Cybersecurity Act (NIS2) and the GDPR. And if you work with production systems and operational technology, IEC 62443 comes into play too. Base27 supports all of these frameworks, and more, from a single platform.

What's the difference between TISAX® and ISO 27001?

ISO 27001 is a broad information security framework that works in any sector. TISAX® takes ISO 27001 as its starting point and adds requirements tailored to automotive, such as the protection of prototypes and partner data.

Is a TISAX® label mandatory?

Not by law. In practice, though, many car manufacturers require one, so without it you risk missing out on contracts.

Does the Cybersecurity Act (NIS2) apply to my organisation?

That depends partly on the size of your organisation and what it does. The manufacture of motor vehicles, trailers and semi-trailers has been designated a critical sector. Even if the law doesn’t apply to you directly, customers who do fall under it may still set requirements for your information security, because they are responsible for securing their supply chain.

What’s the difference between an ISMS and regular security software?

Regular security software, such as a virus scanner, shields your organisation from outside threats. An ISMS takes things further by bringing policies, risk assessments, measures and responsibilities together in one system. The result is not just stronger security, but clear proof that your organisation’s information security is consistently in order.

Can I get support with implementation?

Absolutely. Implementing an ISMS follows a proven approach. You start by defining your information security policy and carrying out a risk assessment. From there, you build awareness across your organisation and prepare for a TISAX® assessment or external audit. Base27 guides you through every stage.